Certificates and proxies
If CloudPouch cannot reach AWS or activate your license from a corporate network while the same profile works at home, your company is probably running TLS inspection. The fix is to point CloudPouch at your company’s CA certificate bundle in PEM format, from Settings → Certificates — or, if you have not activated yet, from the chooser that appears under the certificate error on the Login screen or in the registration dialog. The change applies to new connections and the next scan; you do not need to restart CloudPouch.
Most users never need this setting. On a normal network, CloudPouch connects to AWS APIs directly and the standard certificate chain just works.
Why this happens
Section titled “Why this happens”Enterprise networks often route outbound HTTPS through a security appliance that decrypts the traffic, scans it, and re-signs it with an internal certificate authority. Common products that do this:
- Zscaler Internet Access
- Blue Coat / Symantec ProxySG
- F5 BIG-IP SSL Orchestrator
Your browser trusts the internal CA because IT installed it in the operating system trust store. Desktop applications that bundle their own trust chain do not, so their HTTPS connections fail with certificate errors. CloudPouch solves this by letting you supply the internal CA certificate explicitly.
”License expired” or a connection error that is really a certificate
Section titled “”License expired” or a connection error that is really a certificate”TLS inspection breaks CloudPouch’s licensing calls before it breaks anything else. CloudPouch names that failure with its own error code, TLS_CERTIFICATE_ERROR, and main.log shows self signed certificate in certificate chain alongside it.
That error appears on both licensing paths — the Login screen and the registration dialog — instead of a generic connection failure or an expired-license message. If you see TLS_CERTIFICATE_ERROR, get your company’s CA bundle in PEM format and work through the steps below.
If a licensing failure reports something else, read the reported error before you change any certificate setting: not every licensing problem on a corporate network is a certificate problem. Older CloudPouch versions did not name this failure at all and showed an expired license or a connection error in its place, so on an older version check main.log for the certificate line before ruling certificates out.
Apply the bundle in Settings
Section titled “Apply the bundle in Settings”Settings → Certificates is where you configure the bundle once CloudPouch is activated. Open Settings from the header’s gear menu, or press Cmd/Ctrl + ,, then select Certificates on the left.
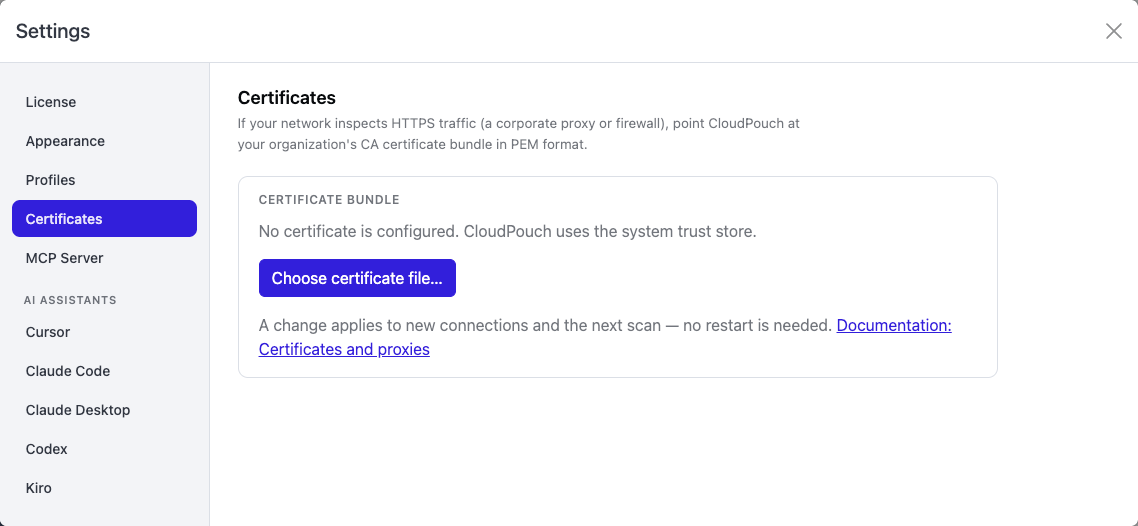
The screenshot shows the default state: No certificate is configured. CloudPouch uses the system trust store. Choose Choose certificate file… to select your company’s PEM bundle. Once configured, this panel shows the file’s full path. Select the screenshot to open it at full resolution.
The panel provides:
- Choose certificate file…, which opens your operating system’s file picker.
- Clear, available when a certificate is configured, which removes the setting and returns CloudPouch to the system trust store.
- A link back to this page.
What the file has to be:
- An absolute path to a file, including the file name — not a directory and not a relative path.
- PEM format. Ask your IT or security team for the CA bundle they use for TLS inspection; it is the same one installed in your browser’s trust store.
- Readable by your user account.
CloudPouch warns you separately when the configured file has disappeared and when it is not a usable PEM bundle. A saved bundle applies to new connections and the next scan — there is no restart step.
CloudPouch stores the setting as certificatePath in config.json (see Local files for the exact paths):
{ "certificatePath": "<Path to your .pem certificate file>"}Custom certificate support is available in CloudPouch 1.25.0 and later.
The file picker, the PEM check, and the write to config.json all happen in CloudPouch’s main process. Settings displays the path of the configured file, but the interface never sends a file path into those operations and never sees the certificate’s contents.
Fix it before you can reach Settings
Section titled “Fix it before you can reach Settings”Settings sits behind activation, and TLS inspection breaks licensing before you ever get there — which is exactly when most people meet this problem. So the same chooser appears on both pre-activation screens, under the certificate error:
- On the Login screen. Applying a bundle that works re-runs license validation immediately.
- In the registration dialog. Applying a bundle that works clears the error so you can submit the form again.
Both screens also show a Clear certificate config button whenever a certificate is already configured.
A wrong bundle locks you out — and how to get back
Section titled “A wrong bundle locks you out — and how to get back”CloudPouch checks that the file you choose is a parseable PEM bundle. It cannot check that it is the right bundle. A wrong-but-valid bundle is accepted and then fails every licensing call, which also keeps you out of Settings.
That is what Clear certificate config on the Login screen and in the registration dialog is for. Clear the setting, CloudPouch goes back to the system trust store, and you can apply the correct bundle. The failure looks unrecoverable otherwise; it is not.
Still failing after configuration
Section titled “Still failing after configuration”Check, in order: the path is exactly right, the PEM file opens in a text editor and starts with -----BEGIN CERTIFICATE-----, and the bundle actually contains the CA your network re-signs with. main.log (see Local files) records connection errors that help narrow down which of these it is.
CloudPouch reads certificatePath and nothing else for this: AWS_CA_BUNDLE and NODE_EXTRA_CA_CERTS are ignored, so setting them has no effect.
Config file locations
Section titled “Config file locations”| Operating system | Config file |
|---|---|
| macOS | /Users/<YOUR_USER_NAME>/Library/Application Support/CloudPouch/config.json |
| Windows | C:\Users\<YOUR_USER_NAME>\AppData\Roaming\CloudPouch\config.json |
| Linux | ~/.config/CloudPouch/config.json |